Products / Technology
Spring Security Scaffolding
Generated authentication and authorization for a Skyway application, including the filter chain, login screens and role checks.
Security scaffolding
Security generated with the screens
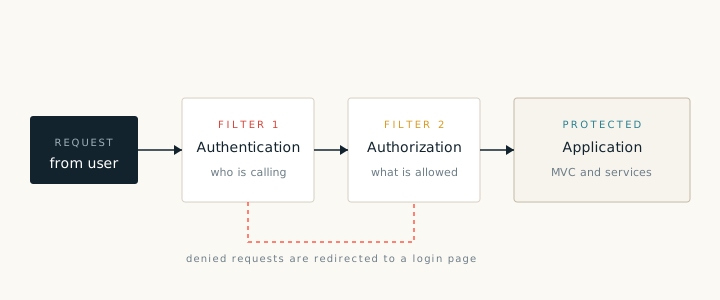
Security scaffolding adds authentication and authorization to a generated application. It writes the filter chain, the login and logout pages, the user and role types and the access rules for each generated screen.
- Authentication against a database, LDAP or an in memory store.
- Role checks per screen and per operation.
- Login, logout and access denied pages.
- Password encoding configured at the security layer.
Who is calling
Authentication establishes the current user before a request reaches a controller. The generated configuration uses a provider that matches the chosen store.
What is allowed
Authorization rules map roles to paths. Keep the rules close to the screens they protect so that a new screen is never left open by accident.
What is recorded
Log successful and failed sign in attempts. A short audit trail makes an access problem much easier to diagnose.